The Start of the Maltego CTF Championship: Qualifier A 🔗︎
On September 12, 2026, the Maltego CTF Championship kicked off with Qualifier A, giving participants four hours to tackle 60 investigation challenges spanning geolocation, chronolocation, maritime and aviation tracking, person-of-interest investigations, due diligence, social media analysis, and brand protection. The round put investigative thinking, resourcefulness, and teamwork to the test as participants worked through unfamiliar scenarios against the clock.
Congratulations to SE4L, Lv1x, and Pinja teams for securing the top three spots—and thank you to everyone who joined us!
Whether you competed, got stuck on a particular challenge, or are preparing for your first CTF, try solving each challenge on your own before reading the walkthrough. Then compare approaches, explore new techniques, and strengthen your investigative workflows. Let’s get started!
Name: Who's Suing? | Category: Due Diligence | 300 pts
Challenge: During a corporate due diligence investigation, OSINT investigators uncovered evidence suggesting that a company associated with Norberto Baesso Hilario became involved in legal proceedings during 2023. Investigators believe the lawsuit may reveal additional connections relevant to the case. Your task is to identify the civil action and determine the identity of the individual who initiated the legal proceedings.
What is the name of the plaintiff who filed a lawsuit against the company whose director is Norberto Baesso Hilario on 19 April 2023?
Answer format: flag{first middle and last name} — underscore not required. Example: flag{John A Smith}
Walkthrough: Searching for the name Norberto Baesso Hilario on OpenCorporates reveals that he is listed as a partner/manager of a company called KOPSCH CONFECÇÕES EIRELI. Performing a targeted Google search using the query "KOPSCH CONFECCOES" "2023" "19" yields a Portuguese PDF document in the search results. Opening this file and searching for "KOPSCH" reveals key case details, including the lawsuit date and the plaintiff's name.
Accepted flags:
flag{ELAINE ROSA GAMA CAMPOI MEI}flag{ELAINE ROSA GAMA CAMPOI}
Name: Historical Handle | Category: Social Media | 200 pts
Challenge: During an online threat intelligence investigation, analysts discovered a Telegram channel involved in the trading of social media accounts and offering account closure services. While reviewing messages and activity logs from the channel, investigators identified references to a Telegram account that had changed its identity.
What was the Telegram username associated with the account @kk4k44 in September 2024?
Answer format: flag{@username}
Walkthrough: First, retrieve the numeric user ID associated with the target Telegram account. Log into Telegram Web, search for the username, and open the profile chat — the user ID will be visible in the browser address bar. Copy this ID and paste it into the SangMata Telegram bot (@SangMata_BOT), which queries past database logs to reveal historical display names and usernames used by that account.
Accepted flags:
flag{QOK6L}flag{@QOK6L}flag{@qok6l}flag{qok6l}
Name: Where Did It Land? | Category: Due Diligence | 300 pts
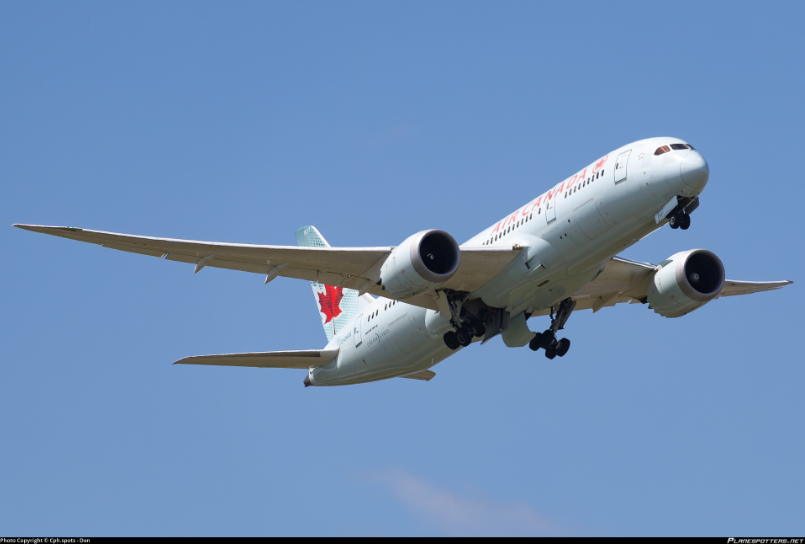
Challenge: During the investigation into the suspect's movements, authorities uncovered a photograph of an aircraft believed to be connected to the suspect's travel. The image is attached to this challenge. Investigators must analyze the photograph and use open-source aviation intelligence to identify the aircraft and trace its movements on the relevant date.
At which airport was this aircraft located on 11 February 2025 at around 11:00 UTC?
Note: Submit the airport code only.
Answer format: flag{ABC}
Walkthrough: Examining the image reveals the aircraft tail number (registration C-GHQQ). Searching for C-GHQQ on ADS-B Exchange and filtering historical data for 11 February 2025 at 11:00 UTC confirms that the aircraft was located at Toronto Pearson International Airport (YYZ/CYYZ).
Since the question had the wrong date, the following answers were also accepted:
Accepted flags:
flag{YUL}flag{YYZ}flag{CYYZ}
Name: Lost at Sea - 1 | Category: Maritime | 100 pts
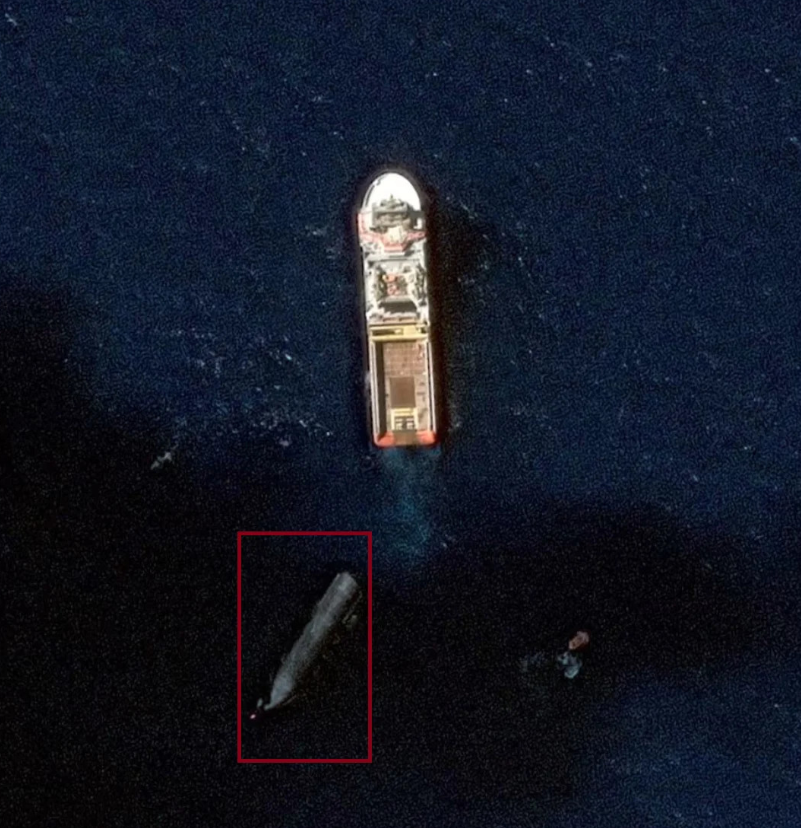
Challenge: You are an intelligence analyst who has received a high-resolution satellite image showing two unidentified objects in the middle of the open ocean. Your mission is to identify both objects using OSINT techniques.
Identify the object highlighted inside the red square. Your answer should include the object's type/name and its associated number. For example, if the object is identified as Submarine 23, the flag should be flag{Submarine_23}
Walkthrough: At first glance, the object visually resembles a large rocket or spacecraft positioned on a barge in the open ocean. Performing a reverse image search using the cropped image identifies multiple publicly available articles and reports discussing offshore transportation of SpaceX hardware with matching satellite imagery, identifying the object as SpaceX Ship 40 (Starship 40). This can also be confirmed by searching the complete satellite image on platforms such as SOAR.
Flag: flag{SHIP_40}
Name: Lost at Sea - 2 | Category: Maritime | 100 pts
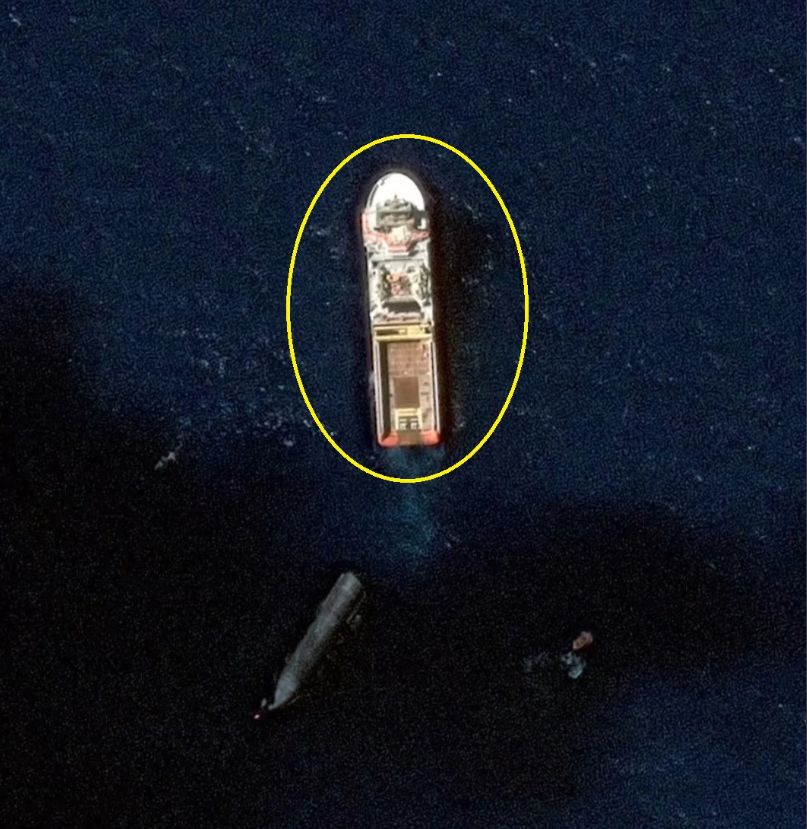
Challenge: Identify the vessel marked in the image and determine its IMO number. If the vessel's name is Atlas and its IMO number is 1234567, the flag should be: flag{Atlas_1234567}
Walkthrough: The reports identified in Task 1 mention that the Starship hardware was being transported by the tug vessel Normand Ranger. Searching for Normand Ranger in a maritime vessel tracking platform such as MarineTraffic, VesselFinder, or Equasis reveals its identifying information, including the IMO number.
Vessel Name: Normand Ranger | IMO Number: 9413432
Source: https://edition.cnn.com/2026/08/03/science/spacex-starship-indian-ocean-recovery-satellite-images
Accepted flags:
flag{Normand_Ranger_9413432}flag{NORMAND_RANGER_9413432}
Name: Crowd on the Horizon - 1 | Category: Physical Security | 100 pts
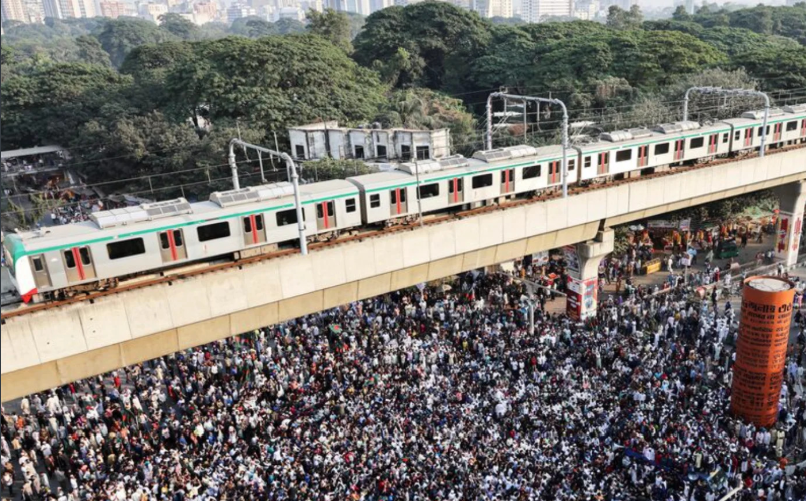
Challenge: You are an intelligence analyst supporting a VIP convoy protection team. Before the convoy begins its movement, your team receives an image showing an ongoing public protest. Your role is to assess the situation and provide actionable intelligence that could impact route planning and operational security.
Determine the country where the protest is taking place.
Flag format: flag{Country_Name}
Walkthrough: Visible clues include pillars and public infrastructure, text in a local language, a metro station and surrounding urban landscape, and other characteristics commonly associated with Asian cities, suggesting the protest is somewhere in Asia. Zooming in further reveals a partially visible flag in the background that, though slightly blurred, strongly indicates Bangladesh.
Flag: flag{BANGLADESH}
Name: Crowd on the Horizon - 2 | Category: Physical Security | 200 pts
Challenge: Identify the primary cause or trigger of the protest. Understanding the underlying issue helps assess the protest's potential intensity, duration, and likelihood of escalation, enabling the convoy team to make informed operational decisions.
Submit the name of the key individual directly associated with the identified trigger. For example, if the individual is John Doe, the flag would be flag{John_Doe}.
Walkthrough: Using Bangladesh as the primary search term, search for recent news articles containing images resembling the one provided. Comparing the crowd, banners, location, and surrounding environment with news coverage helps identify the specific protest event. Cross-referencing against open-source event databases such as the Global Protest Tracker reveals the protest was triggered by the killing of Sharif Osman Bin Hadi.
Source: https://carnegieendowment.org/features/global-protest-tracker
Accepted flags:
flag{SHARIF_OSMAN_BIN_HADI}flag{OSMAN_HADI}flag{OSMAN_GONI}
Name: From Photo to Footprint - 1 | Category: Social Media | 200 pts
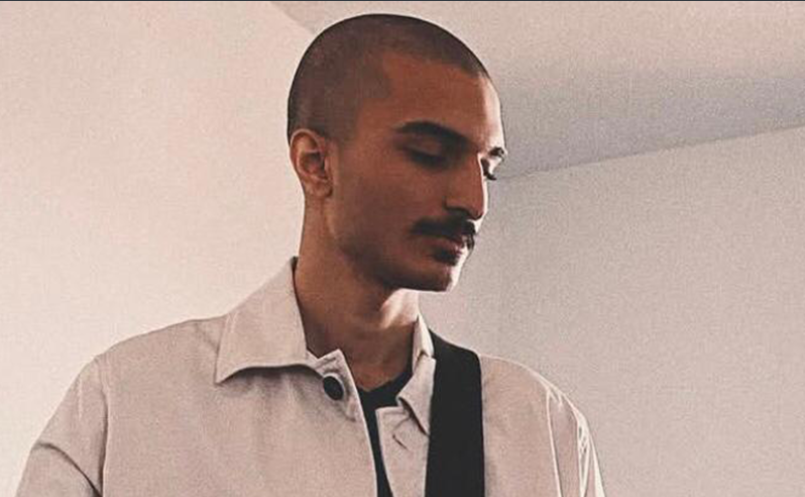
Challenge: During an ongoing police investigation, officers received only a facial photograph of a potential suspect from an anonymous source. No identifying information such as a name, email address, or phone number was provided. Investigators must leverage OSINT techniques to trace the individual's digital footprint, uncover their identity, and identify any publicly available information linked to the suspect.
What is this person's personal email address?
Answer format: flag{email@example.com}
Walkthrough: Performing a reverse image search reveals the target's name, Humam Abo Alraja, and leads to his social media profiles, including LinkedIn. To discover his email address, generate potential pattern combinations across major providers (e.g., @gmail.com, @outlook.com) or use LinkedIn email lookup extensions such as ContactOut or SignalHire.
Flag: flag{HUMAMABOALRAJA@GMAIL.COM}
Name: From Photo to Footprint - 2 | Category: Social Media | 300 pts
Challenge: What was the username of the deleted X (formerly Twitter) account that this person previously used?
Answer format: flag{@username}
Walkthrough: Leveraging the target's LinkedIn profile with a browser extension like SignalHire reveals two associated X (formerly Twitter) accounts: @humamaboalraja and @HomamAlhasan.
Flag: flag{@HOMAMALHASAN}
Name: Who's the Host? | Category: Social Media | 200 pts
Challenge: Further analysis revealed that the suspect had rented an Airbnb property. To gather additional information about the suspect's stay, investigators need to identify and contact the property owner or listing host associated with the rental.
What is the full name of the Airbnb apartment owner (host/lister)?
Link: https://www.airbnb.com/rooms/24881666
Answer format: flag{first last} — underscore not required
Walkthrough: Navigate to the provided link and visit the host's profile page. Open your browser's Developer Tools (Inspect Element) to extract the full direct URL of the profile image. Running a reverse image search on this image URL unveils matching profiles across multiple social media platforms, revealing the host's actual name.
Accepted flags:
flag{GERALD SCHÖNBUCHER}flag{GERALD SCHOENBUCHER}
Name: Beyond the Domain - 1 | Category: Threat Intelligence | 100 pts
Challenge: You are working as a Threat Intelligence Investigator conducting an external attack-surface assessment for BDO Germany. Your objective is to identify publicly exposed infrastructure and third-party services that could potentially provide useful information to threat actors targeting the company. Understanding this infrastructure can help the security team identify potential exposure and reduce the risk of phishing, impersonation, and other targeted attacks.
Which email service is used by bdo.de?
Answer format: flag{email service} — underscore not required
Walkthrough: Searching for BDO Germany reveals their official website, bdo.de. Performing DNS reconnaissance using a platform like DNSDumpster reveals an MX record pointing to mx2.hc697-83.eu.iphmx.com. Searching for this hostname indicates the organization utilizes Cisco Secure Email (formerly Cisco IronPort).
Accepted flags:
flag{cisco email}flag{cisco secure}flag{cisco secure email}flag{cisco email security}flag{cisco ironport}flag{ironport}
Name: Beyond the Domain - 2 | Category: Threat Intelligence | 200 pts
Challenge: Which two additional domains can be associated with bdo.de?
Answer format: flag{website1.com,website2.com}
Walkthrough: Navigating to bdo.de and examining its source code reveals an embedded Google Tag. Performing a reverse search on this Google Tag using a tool like DNSlytics uncovers two additional websites using the exact same tag ID.
Accepted flags:
flag{bdo-oldenburg.de,bdo-tuc.de}flag{bdo-tuc.de,bdo-oldenburg.de}
www. and http/s prefixes are also accepted.
Note: "Beyond the Domain - 1 & 2" (MX record lookup, then reverse-searching a Google Tag ID to find related domains) could be visualized using Maltego Graph connecting a domain to its MX records, then pivoting from a Google Tag ID to sibling domains. It's core infrastructure/affiliate-mapping investigation (domain → MX → Tag ID → related domains), using Maltego's Transforms for DNS and tracking-code pivoting.
Name: Shadow Brand - 1 | Category: Brand Protection | 200 pts
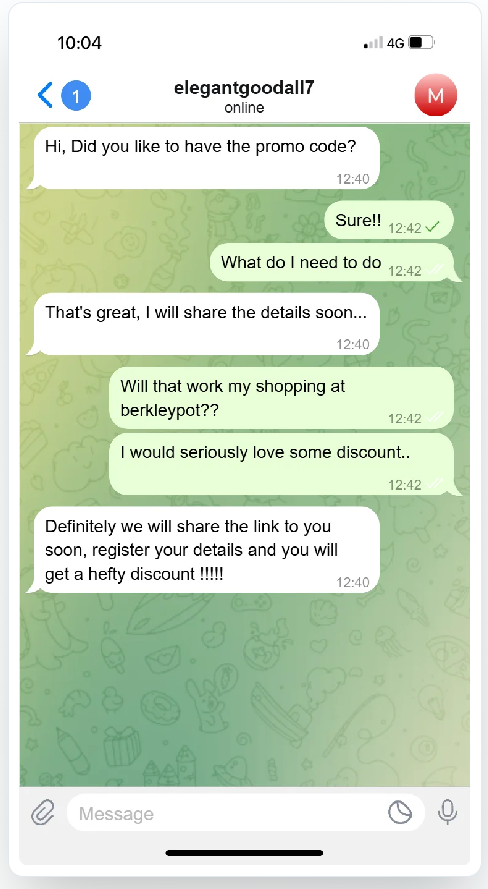
Challenge: Intelligence suggests that threat actors are impersonating the brand across multiple online platforms to lure victims into fraudulent websites. During the investigation, you receive a screenshot of a conversation between a scammer and a victim. Unfortunately, the message containing the malicious URL has been deleted before it could be captured. Your objective is to use the available evidence and OSINT techniques to uncover the remaining infrastructure used by the threat actors.
Note: Do not access the domain, as it may be potentially dangerous.
Determine another social media platform where the threat actor or scam group is actively promoting its fraudulent campaign. If the platform is Instagram, the flag would be: flag{Instagram}
Walkthrough: The only artifact provided is a screenshot of a Telegram conversation showing a display name and username. Since usernames are often reused across platforms, they provide a strong pivot point. Using SOCMINT tools and username search techniques reveals a matching profile on Bluesky: https://bsky.app/profile/elegantgoodall7.bsky.social, matching the username observed in the Telegram conversation.
Accepted flags:
flag{Bluesky}flag{bsky}
Name: Shadow Brand - 2 | Category: Brand Protection | 100 pts
Challenge: Using the information gathered from the first task, identify the typosquatted domain being used by the threat actors to redirect victims to their phishing website. If the legitimate domain is google and the threat actor uses go0gle, the flag would be: flag{go0gle}
Walkthrough: Reviewing the Bluesky profile's posts, replies, and comment threads reveals a comment referencing the domain berkleyopt. In the original Telegram conversation, the scammer was discussing berkleypot. Comparing the two names reveals a subtle character transposition, a common typosquatting technique, confirming berkleyopt as the fraudulent domain.
Flag: flag{berkleyopt}
Name: Following the Bitcoin Trail - 1 | Category: Fraud | 200 pts
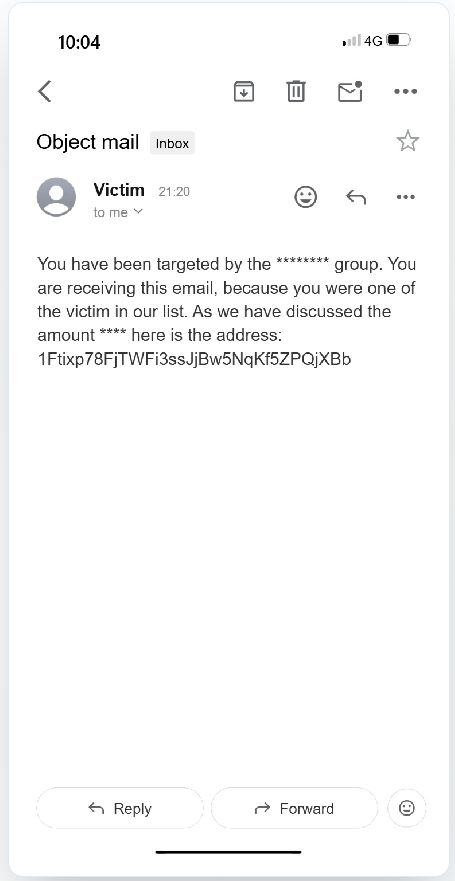
Challenge: You are a cyber threat intelligence analyst investigating a large-scale online fraud campaign. The only evidence recovered so far is a screenshot containing an email address believed to be associated with the threat actor. Begin your investigation using the evidence provided. Trace the associated Bitcoin transaction and identify the wallet address that appears in the transaction inputs. Intelligence indicates that the transaction contains a large number of inputs.
Answer format: flag{1A2b3C}
Walkthrough: The screenshot contains a Bitcoin wallet address, the starting point for the investigation. Searching the wallet address using a blockchain explorer such as WalletExplorer shows two transactions. Since the challenge specifies the transaction was received, inspect the incoming transaction. Opening it reveals a large number of input addresses; one address appears repeatedly, contributing multiple inputs: 1Mz7153HMuxXTuR2R1t78mGSdzaAtNbBWX.
Flag: flag{1Mz7153HMuxXTuR2R1t78mGSdzaAtNbBWX}
Name: Following the Bitcoin Trail - 2 | Category: Fraud | 100 pts
Challenge: After locating the transaction, analyze the list of transaction inputs. Determine the amount of Bitcoin associated with Input 45 (the final input in the transaction). Example: if the value of Input 45 is 1.234 BTC, the flag would be flag{1.234}
Walkthrough: While viewing the transaction details in the blockchain explorer, navigate to the final input (Input 45), where the corresponding Bitcoin amount is displayed: 0.0022139 BTC.
Accepted flags:
flag{0.0022139}flag{0.00221390}
Name: Following the Bitcoin Trail - 3 | Category: Fraud | 300 pts
Challenge: Intelligence suggests that the threat group might use another Bitcoin wallet to pay for premium subscriptions on paste-sharing platforms or other online services, allowing them to continue publishing announcements and communicating with victims. Using the intelligence gathered during the previous tasks, identify this additional Bitcoin wallet address. If the wallet address is 1A2b3C, the flag would be: flag{1A2b3C}
Walkthrough: At this stage, two wallet addresses and the transaction timing are known and can be used as pivot points. Searching the wallet addresses, transaction details, and related indicators leads to reports linking the activity to the NotPetya ransomware campaign. Visiting RansomLook.io's Crypto section and searching for the NotPetya group lists multiple associated Bitcoin wallets, including an additional wallet not previously identified: 13KBb1G7pkqcJcxpRHg387roBj2NX7Ufyf.
Flag: flag{13KBb1G7pkqcJcxpRHg387roBj2NX7Ufyf}
Name: Finding the Author | Category: Due Diligence | 100 pts
Challenge: During an OSINT investigation, analysts are tracking the digital footprint of an individual known as Bob Fabien "BZ" Zinga. Investigators believe that a resume associated with this individual has been shared online and need to identify the source behind its publication.
What is the Google GAIA ID of the email account that posted the Bob Fabien "BZ" Zinga resume?
Answer format: flag{109482039184750293817}
Walkthrough: Searching for "Bob Fabien 'BZ' Zinga resume" reveals the target's resume hosted on Google Docs. Extracting the Google Doc ID from the URL (1OP5rj77-WWBAbhoublqxScD851Y0xgxVKx5OA-TKd_4) and inputting it into an OSINT tool like GHunt identifies the Google account details of the document's uploader.
Flag: flag{02388806070359922223}
Name: WiFi Footprint | Category: Threat Intelligence | 100 pts
Challenge: Following the arrest of a suspect, digital forensics investigators examined the suspect's mobile phone and recovered information about a previously connected WiFi network. The network was associated with the password "klrt0713", but its physical location was unknown. Investigators believe that identifying the wireless access point associated with this network could help determine where the suspect had been staying or residing.
Using the recovered WiFi information, determine in which city the suspect was living.
Answer format: flag{AP Name} — underscore not required
Walkthrough: Searching for the Wi-Fi password "klrt0713" in Wi-Fi databases such as P3WiFi reveals the wireless MAC address and associated coordinates. Opening the coordinates on a map identifies the town where the access point is located.
Accepted flags:
flag{KRANJSKA_GORA}flag{KRANJSKA GORA}
Name: The Disappeared Website | Category: Trust & Safety | 200 pts
Challenge: You work as a Threat Intelligence Investigator for CHRIST, a well-known German jewelry and watch retailer. During an investigation into online brand impersonation, your team has identified evidence of a fraudulent website that was active in September 2023 and closely replicated the design and template of the official christ.de website. The impersonating website is no longer accessible, so investigators must rely on historical records and archived webpages to identify the fraudulent domain and uncover additional information about the operation.
What was the domain name of the impersonating website in September 2023?
Answer format: flag{website.com}
Walkthrough: One method for identifying an impersonating website is a favicon search: obtain the target website's favicon and calculate its MD5 hash, or use a service such as Favicon Hash to obtain the hash. The resulting hash can then be searched via a service such as SilentPush to find other domains/websites reusing the same favicon, helping identify phishing or impersonating websites.
Flag: flag{ultraper.click}
Name: The Hidden Alias - 1 | Category: Fraud | 100 pts
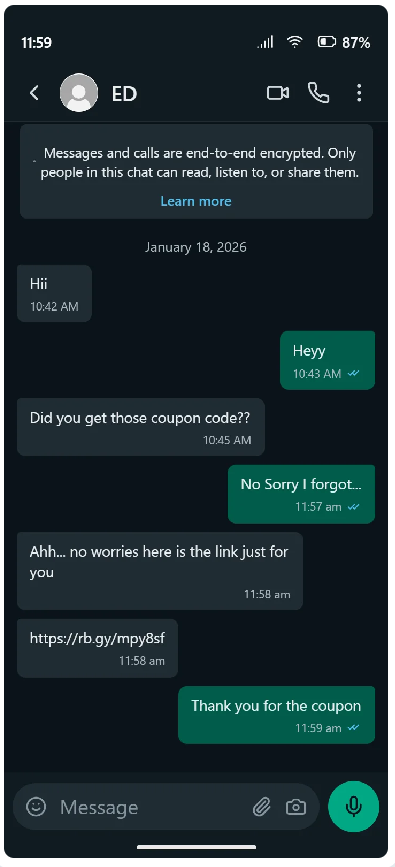
Challenge: A victim has reported a suspected fraud scam conducted through WhatsApp. As part of the investigation, you have been provided with a screenshot/export of the victim's WhatsApp conversation with the suspected scammer.
Examine the provided WhatsApp conversation and identify the username/online alias being used by the suspected scammer.
Flag format: flag{username} — e.g. if the username is @test_abc, the flag would be flag{@test_abc}
Walkthrough: At the top of the chat, the only visible identifier is "ED", which is not sufficient on its own. However, the conversation contains a shortened URL: https://rb.gy/mpy8sf, which redirects to an image hosted on ImgBB: https://ibb.co/nqfdVj8B. The voucher image itself appears unremarkable, so the next step is to examine its EXIF metadata using a tool such as the Stego Toolkit EXIF Data Extractor. The metadata reveals the string @ED_led.
Accepted flags:
flag{@ED_LED}flag{ED_LED}
Name: The Hidden Alias - 2 | Category: Fraud | 200 pts
Challenge: Use the username identified in Task 1 to conduct further OSINT research. The investigation indicates that the suspect uses a social-media profile to communicate with people. Pivot across publicly available sources and determine the complete name the individual appears to be using.
Flag format: flag{Firstname_lastname}
Walkthrough: Searching for the username @ED_led across social media platforms leads to a Mastodon profile: https://mastodon.social/@ED_led. Examining the posts and replies associated with the account, an interaction reveals the suspect's complete name: Eddie Ledbetter.
Flag: flag{Eddie_Ledbetter}
Name: The Hidden Alias - 3 | Category: Fraud | 200 pts
Challenge: Further intelligence indicates that the identified individual has previously been convicted in a criminal case in 2026 only. Using the person's identified name and other relevant identifiers, locate the corresponding publicly available correctional/parole record and determine the Inmate Identification Number (AIS/identification number) associated with the individual.
Flag format: flag{123456}
Walkthrough: The suspect's name, Eddie Ledbetter, alone may not be sufficient to reliably locate the correct record, so another identifier is needed. Returning to the Mastodon profile, the account's bio references Alabama, providing the geographic pivot required. Searching Alabama's public parole/correctional records — specifically the Alabama Bureau of Pardons and Paroles' current-year parole results — for Eddie Ledbetter leads to the corresponding inmate record, providing the Inmate Locator ID / AIS number: 262559.
Flag: flag{262559}
Name: The Hidden Telegram Trail | Category: Dark Web | 100 pts
Challenge: The research team has provided you with a .onion URL associated with an underground online operation. Your task is to investigate the provided Tor hidden service and identify the Telegram group associated with the operation.
Link: op7yiekgumt7po6mjgii4uewrwjydx5vhpa6y5gv7glftmw5srbwnaid\\\\\\[.]onion
OPSEC Note: Exercise caution when accessing the .onion link; use proper OPSEC and rely on OSINT techniques to solve the challenge without interacting with suspicious content.
Flag format: flag{GroupName}
Walkthrough: Rather than directly accessing the hidden service, use OSINT techniques and Google dorking to search for references to the onion address. The results lead to reports and Telegram-related intelligence, including a Telegram OSINT page at https://tgstat.ru/channel/@noname05716rus, which reveals the associated Telegram channel name as NoName057(16)🇷🇺.
Accepted flags:
flag{NONAME057(16)}flag{NONAME057}
Name: Echoes in the Dark - 1 | Category: Dark Web | 200 pts
Challenge: While monitoring dark-web forums, the research team discovered an image being shared in connection with a well-known threat group. The team suspects that the image contains embedded information that can provide additional intelligence about the group.
Source: https://ibb.co/gMWjTY47
Analyze the provided image using appropriate image-forensics and OSINT techniques. Identify the information embedded within the image and use it to establish the connection to the threat group. The investigation should ultimately reveal an email address associated with the group using the @tutanota.com domain.
Flag format: flag{email@example.com} — for example, flag{abc@tutanota.com}
Walkthrough: Analyzing the image using a steganography tool such as the Stego Toolkit Text in Image Extractor reveals an encoded string using ROT13: fnagng7xcyyg6vlidoe7d4nzqi6qmeu6cnngilemy7el3mz72mvts4nq.bavba. Decoding this with a ROT13 decoder reveals the .onion address santat7kpllt6iyvqbr7q4amdv6dzrh6paatvyrzl7ry3zm72zigf4ad.onion. Pivoting on this onion address using search-engine dorking uncovers references linking the infrastructure to the Clop ransomware group. Pivoting to Ransomware.live's Clop group page and examining the IOC information reveals the email indicator managersmaers@tutanota.com.
Flag: flag{managersmaers@tutanota.com}
Name: Echoes in the Dark - 2 | Category: Dark Web | 300 pts
Challenge: The investigation then moves to the torrent infrastructure associated with the same threat group. The research team has identified the following torrent infohash as being linked to the group: 3972dd9c063f297dbaf386d1bcae235a2d0142dd
Reports indicate that activity associated with this torrent occurred on 25 July 2026 and involved port 11369. Your task is to investigate the available torrent/peer intelligence for the specified date and port, identify the relevant peer IP address, and then determine the Autonomous System Number (ASN) associated with that IP address.
Flag format: flag{AS1234}
Walkthrough: Having already established a connection to the Clop group, pivot to RansomLook and search for the provided infohash. The result is associated with the Clop group, confirming the previous finding. Opening the corresponding torrent intelligence record and navigating to the records for 25 July 2026 identifies the peer associated with port 11369: IP address 31.217.177.172. Pivoting on the IP using Cloudflare Radar's IP lookup (https://radar.cloudflare.com/ip/31.217.177.172) identifies the ASN as AS6799.
Flag: flag{AS6799}
Name: The Counterfeit Web - 1 | Category: Brand Protection | 100 pts
Challenge: Threat intelligence reports indicate that alphazoneshop\\\\\\[.]com may be associated with a phishing campaign and counterfeit activity. Your task is to investigate the domain using passive OSINT and domain-intelligence techniques to uncover information about the infrastructure and identify the brand being targeted.
Your objective is to identify the privacy/customer service phone number associated with the domain.
Flag format: flag{XXXXXXXX}
Walkthrough: Analyzing the domain using Maltego's domain and WHOIS-related search capabilities reveals registration/contact information associated with Contact Privacy Inc. Customer 0149296389. The customer identifier is the required value.
Flag: flag{0149296389}
Name: The Counterfeit Web - 2 | Category: Brand Protection | 200 pts
Challenge: Investigate the domain's history, related domains, and search-engine results. Identify the brand/company being targeted through phishing or counterfeit domains.
Flag format: flag{CompanyName}
Walkthrough: Investigating the domain using VirusTotal and analyzing the available URL intelligence and detection results identifies reports indicating that the domain is associated with impersonation or targeting of Amazon.com.
Flag: flag{Amazon}
Name: Flags, Ports & Detentions - 1 | Category: Maritime | 200 pts
Challenge: Your maritime intelligence team has intercepted the radio callsign TJM7W3. The callsign is believed to be associated with a commercial vessel that requires further investigation. Identify the vessel associated with callsign TJM7W3 and investigate its historical flag, AIS, and port-call information.
Determine which port the vessel visited on 14 January 2026.
Flag format: flag{Port_ABC} where ABC is the identified port name.
Walkthrough: Searching the callsign TJM7W3 on MarineTraffic identifies the vessel as MARVEN, IMO number 9305556. Pivoting to Global Fishing Watch with the IMO number allows examination of previous vessel identities and MMSI information. Examining the historical record for 14 January 2026 shows the vessel track and the recorded port visit: Yarimca.
Accepted flags:
flag{PORT_YARIMCA}flag{YARIMCA_PORT}
Name: Flags, Ports & Detentions - 2 | Category: Maritime | 300 pts
Challenge: Continue the investigation using the vessel's inspection and detention records for 14 January 2026. The vessel was inspected at a nearby port and detained for a deficiency classified as being related to "Not properly maintained." Identify the specific deficiency reported in the inspection record.
Flag format: flag{Type_of_Deficiency}
Walkthrough: Using the previously identified IMO number 9305556, pivot to Equasis and examine the vessel's inspection history. Locating the inspection record for 14 January 2026 and reviewing the Grounds for Detention section, under the "Not properly maintained" category, the reported deficiency is listed as "Emergency fire pump."
Accepted flags:
flag{EMERGENCY_FIRE_PUMP}flag{EMERGENCY FIRE PUMP}
Name: The Metro Trail | Category: Physical Security | 300 pts
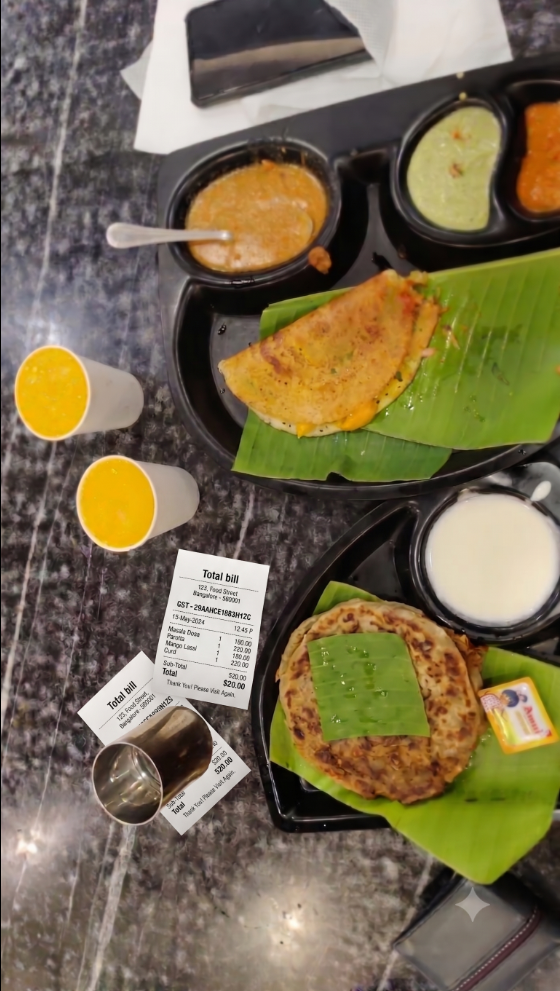
Challenge: The intelligence team has shared an image with you that was captured outside the hotel where an upcoming conference is scheduled to take place. The team suspects that two persons of interest travelled to the conference venue using a nearby metro station. Your task is to analyze the photograph and identify the metro station that most likely served as their point of departure.
Flag format: FLAG{METROSTATIONNAME}
Walkthrough: The image contains a food item along with a bill, and the key pivot point is the GST number 29AAHCE1883H1ZC printed on the bill. Searching this GST number leads to ESSOTTO PRIVATE LIMITED, with the address PLOT NO. 120, ITPL BMTC Bus Station, EPIP AREA, Near Vydehi Hospital, Whitefield, Bengaluru Urban, Karnataka – 560066. Searching this address on Google Maps identifies the nearby metro station, Nallur Halli Metro Station.
Source: https://fnshiftsolutions.com/gstin-search/essotto-private-limited-29AAHCE1883H1ZC
Accepted flags:
flag{NALLURHALLI}flag{NALLUR HALLI}flag{NALLUR_HALLI}
Name: Secure Shelter | Category: Physical Security | 200 pts
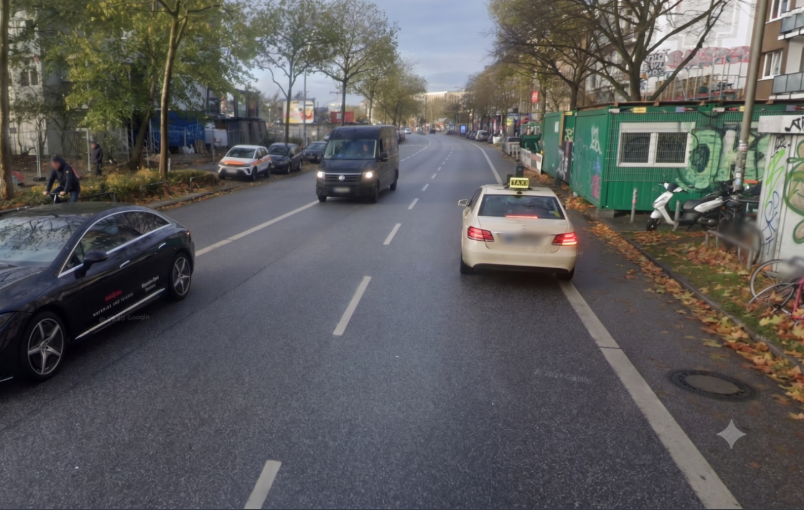
Challenge: The VIP convoy is planning its next trip. Due to ongoing security risks, you have been tasked with identifying a hotel that provides a secured space within or directly integrated into the hotel premises. Your ally has provided you with a possible street-level image of the location. Your task is to investigate the image, identify the hotel, and determine the original name of the secure/sheltered space located above or within the hotel structure.
Flag format: flag{safe_space_name} — for example, if the shelter name is Knight Palace, the flag would be flag{Knight_Palace}
Walkthrough: Analyzing the street image for visual clues — the taxi, road environment, building architecture, and surrounding structures — narrows the location down to Germany. Pivoting toward hotels built on or incorporated into historically protected bunker structures, searching terms such as "Germany hotel bunker" or "Hamburg hotel bunker" leads to the REVERB by Hard Rock Hotel Hamburg, located at Feldstraße 66, Hamburg — a match confirmed against the supplied image and Hamburg tourism information. Further research reveals the hotel is integrated into the historic St. Pauli Bunker (Hochbunker at Feldstraße), originally known as Flakturm IV (Flak Tower IV), one of Hamburg's WWII-era flak towers.
Flag: flag{Flakturm_IV}
Name: The Unknown Hex ID | Category: Maritime | 200 pts
Challenge: You have intercepted a HEX ID from a signal. At first glance, the value appears to be nothing more than a random hexadecimal string, but it may contain an important identifier associated with an aircraft. Your initial task is to determine what the HEX ID represents and use it as the starting point for an aviation OSINT investigation. Once you identify the aircraft associated with the identifier, continue pivoting through publicly available aviation databases and aircraft-registration records to determine who owns or operates the aircraft.
Hex ID: 8DA0551499091184C00400519503
Flag format: flag{complete_owner_or_operator_name} — example: if the operator is Northwest Group of Airlines, submit FLAG{NORTHWEST_GROUP_OF_AIRLINES}. Submit the flag in uppercase letters only, separated by underscore.
Walkthrough: Since the identifier originated from an aviation signal, it may correspond to a Mode-S / ICAO 24-bit aircraft address. Using an ADS-B lookup service such as ADS-B.dev to query the identifier returns the aircraft address A0 55 14. Searching this address in Flightradar24's aircraft database leads to the aircraft N120QD, a Pilatus PC-12/45, with Mode-S address A05514, operated by Quest Diagnostics. Pivoting to the FAA Aircraft Inquiry database with the registration N120QD confirms the registered owner as QUEST DIAGNOSTICS CLINICAL LABORATORIES INC.
Accepted flags:
flag{QUEST_DIAGNOSTICS_CLINICAL_LABORATORIES_INC}flag{QUEST_DIAGNOSTICS_CLINICAL_LABORATORIES}flag{QUEST DIAGNOSTICS CLINICAL LABORATORIES INC}
Name: Flight Trail & Aircraft Connection - 1 | Category: Maritime | 200 pts
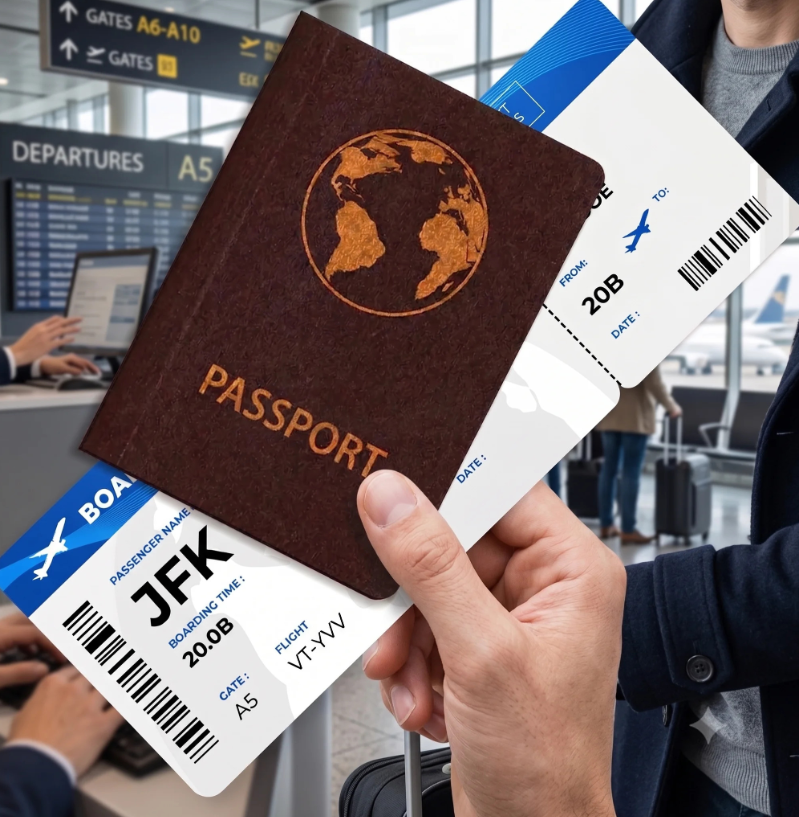
Challenge: Your SOCINT team has provided you with an image containing aviation-related information. Intelligence indicates that the suspect made multiple flights on July 31, 2026. Your task is to analyze the available information and reconstruct the suspect's flight activity for that date. Determine the sequence of flights and identify the last destination city reached by the suspect on July 31, 2026.
Flag format: Flag{City_Name}
Walkthrough: The image provides a boarding pass. The key pivot point is the flight information printed on the pass, particularly the aircraft/registration identifier VT-YVV. Searching VT-YVV on FlightAware and examining its historical flight records allows reconstruction of the aircraft's movements on July 31, 2026. Reviewing the complete sequence of flights for that day chronologically, rather than stopping at the first match, shows the final flight of the day arrived in New Delhi.
Accepted flags:
flag{NEW_DELHI}flag{NEW DELHI}
Name: Flight Trail & Aircraft Connection - 2 | Category: Maritime | 100 pts
Challenge: Your team has also discovered that the airline operator maintains a fleet of multiple aircraft. One of the other aircraft operated by the same organization was involved in a separate aviation incident. You have been provided with the name/model of that aircraft, and your task is to pivot through aviation records and incident reports to identify its tail/registration number.
Aircraft Name: Beechcraft King Air 200
Flag format: flag{TailNumber}
Walkthrough: Searching the aircraft information on Flightradar24 identifies the associated operator as Air Charter Services. Pivoting from the operator to its publicly listed fleet, Air Charter Services' official fleet page identifies the aircraft as Beechcraft King Air 200 VT-FAE, independently corroborated through other aviation fleet data.
Flag: flag{VT-FAE}
Name: Satellite Current Anomaly | Category: Maritime | 300 pts
Challenge: Your satellite intelligence team has intercepted a WAV recording from a satellite. The satellite's onboard systems are suspected of experiencing unusual activity, and the investigation team wants to determine whether there was any abnormal electrical behavior.
Your task is to determine the current drawn by the satellite's On-Board Computer (OBC) on August 5, 2026.
Flag format: flag{Current_mA} — for example, if the OBC current is 12 mA, the flag would be flag{12mA}
Audio recording: https://static.maltego.com/cdn/Community/Challenge-Source-Satellite-Current-Anomaly.wav (paste this)
Walkthrough: The recording contains Morse code rather than conventional satellite telemetry. Using an online Morse audio decoder such as MorseCode.World's Audio Decoder converts the sequence into text, providing NORAD ID 66778. Searching this NORAD ID in the SatNOGS Database identifies the satellite as Foresail-1p, an operational 3U CubeSat developed in Finland. The SatNOGS entry links to the satellite's Telemetry Dashboard; navigating to the EPS (Electrical Power System) section and the Avionics Current data, the OBC Current value recorded on August 5, 2026 is 84 mA.
Flag: flag{84MA}
Name: Identify the Aircraft | Category: Maritime | 200 pts
Challenge: You are investigating an aviation signal intercepted by your team. The signal contains information that can be used to identify the aircraft transmitting it. Your task is to analyze the provided aviation signal, extract the relevant aircraft identifier, and pivot through publicly available aviation databases to determine the complete aircraft model.
Intercepted signal string: /QUKAXBA.ADS.G-VIIW0301072498E7FD3D0021B4DA9F7EC2
Flag format: for example, if the aircraft is a Beechcraft King Air 200(LS), submit flag{Beechcraft_King_Air_200_LS}. Remove any special characters or parentheses and separate each word with an underscore.
Walkthrough: Analyzing the structure and fields within the frame identifies it as an ACARS frame. The ACARS message contains an aircraft registration identifier — the key pivot — which in this case is G-VIIW. Searching this registration on Flightradar24 identifies it as a Boeing 777-236(ER) operated by British Airways, with Mode-S code 400774. This is independently corroborated by other aviation databases such as Plane Finder and Airport-Data, which list it as a Boeing 777-236(ER)/777-236.
Flag: flag{BOEING_777_236_ER}
Name: The Renamed Vessel | Category: Maritime | 300 pts
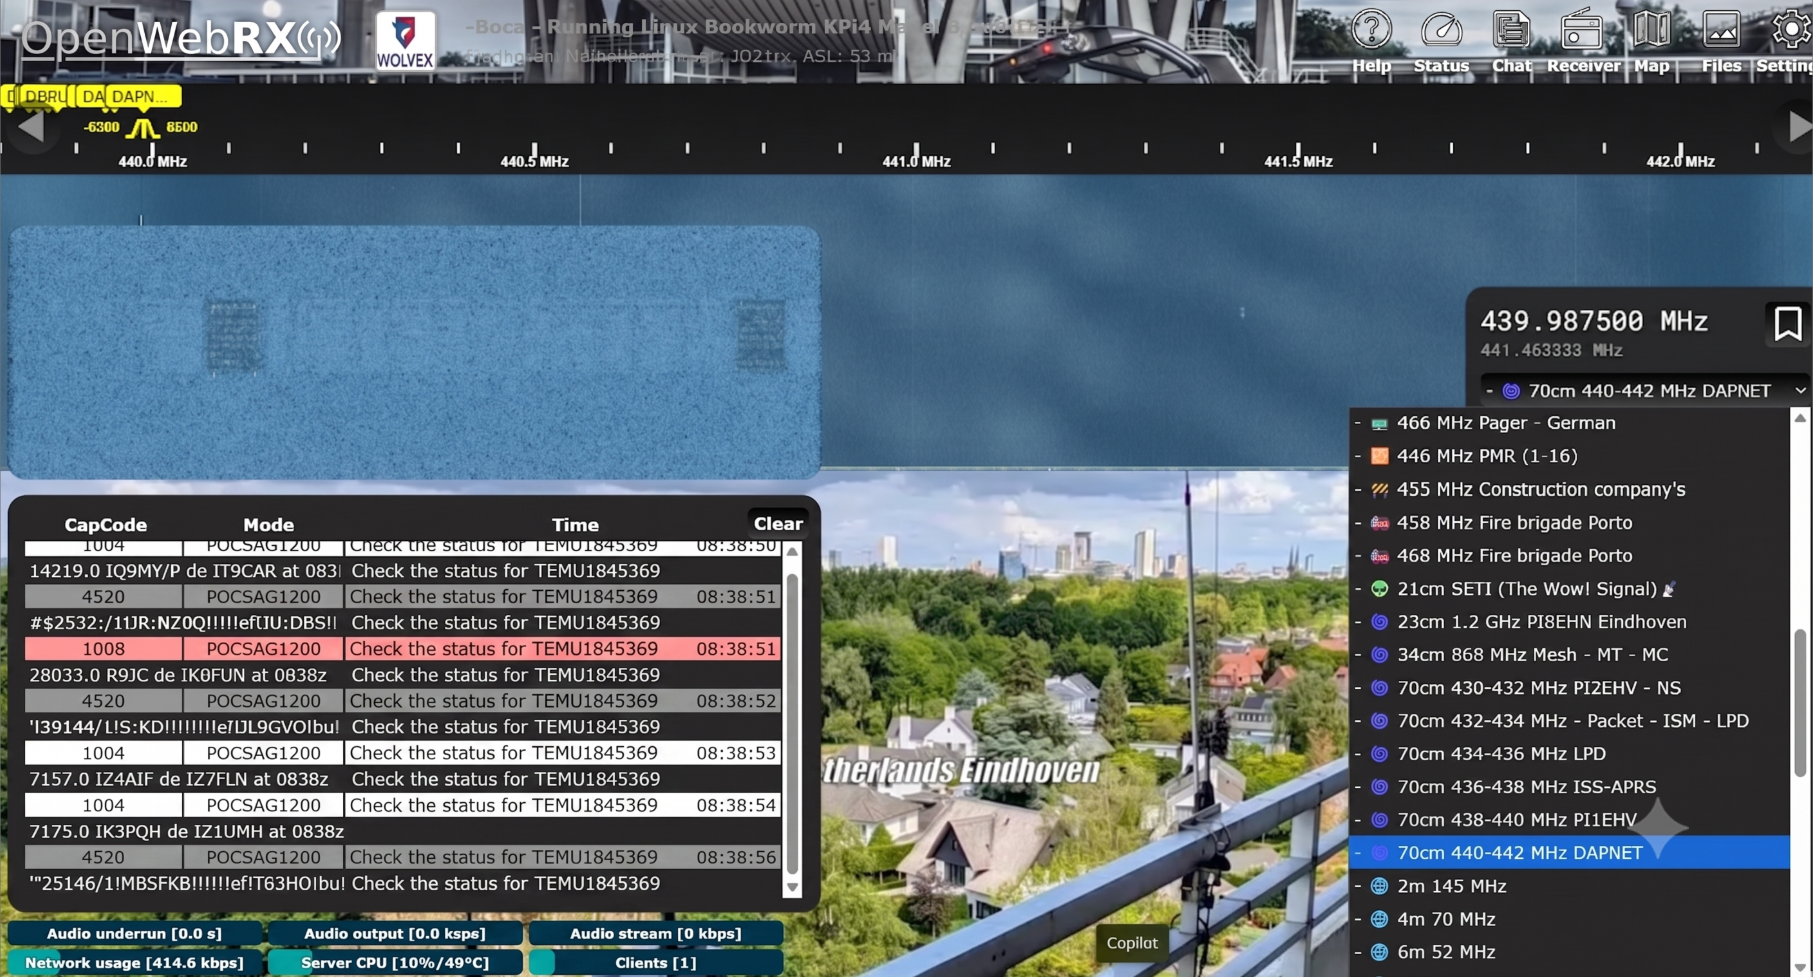
Challenge: Your SDR receiver has intercepted a POCSAG transmission containing information related to a suspicious maritime shipment. The decoded message suggests that a particular vessel may have been involved in transporting the suspicious load. Intelligence indicates that the vessel has changed its name in the past, and the relevant name change occurred in June 2013. Your task is to investigate the vessel's historical records, identify the vessel that underwent the June 2013 name change, and determine the MMSI assigned to the vessel during that historical period.
Flag format: for example, if the historical MMSI is 565286000, the flag would be flag{565286000}
Walkthrough: The challenge begins with an image of a pager device containing the message "Check the status of TEMU1845369." This value is the key pivot: its format identifies it as a shipping container number, with TEMU being the owner prefix. Using a container-tracking service such as TrackTainer, searching for TEMU1845369 provides the container's voyage information, identifying the associated vessel as VELIKA, IMO number 9243162 — independently corroborated through maritime databases. Using the IMO number as a persistent identifier, searching Global Fishing Watch's vessel database and narrowing the timeline to June 2013 exposes historical vessel records, showing the MMSI 367037568 for that period.
Flag: flag{367037568}
Name: The Missing Timestamp - 1 | Category: Chronolocation | 100 pts
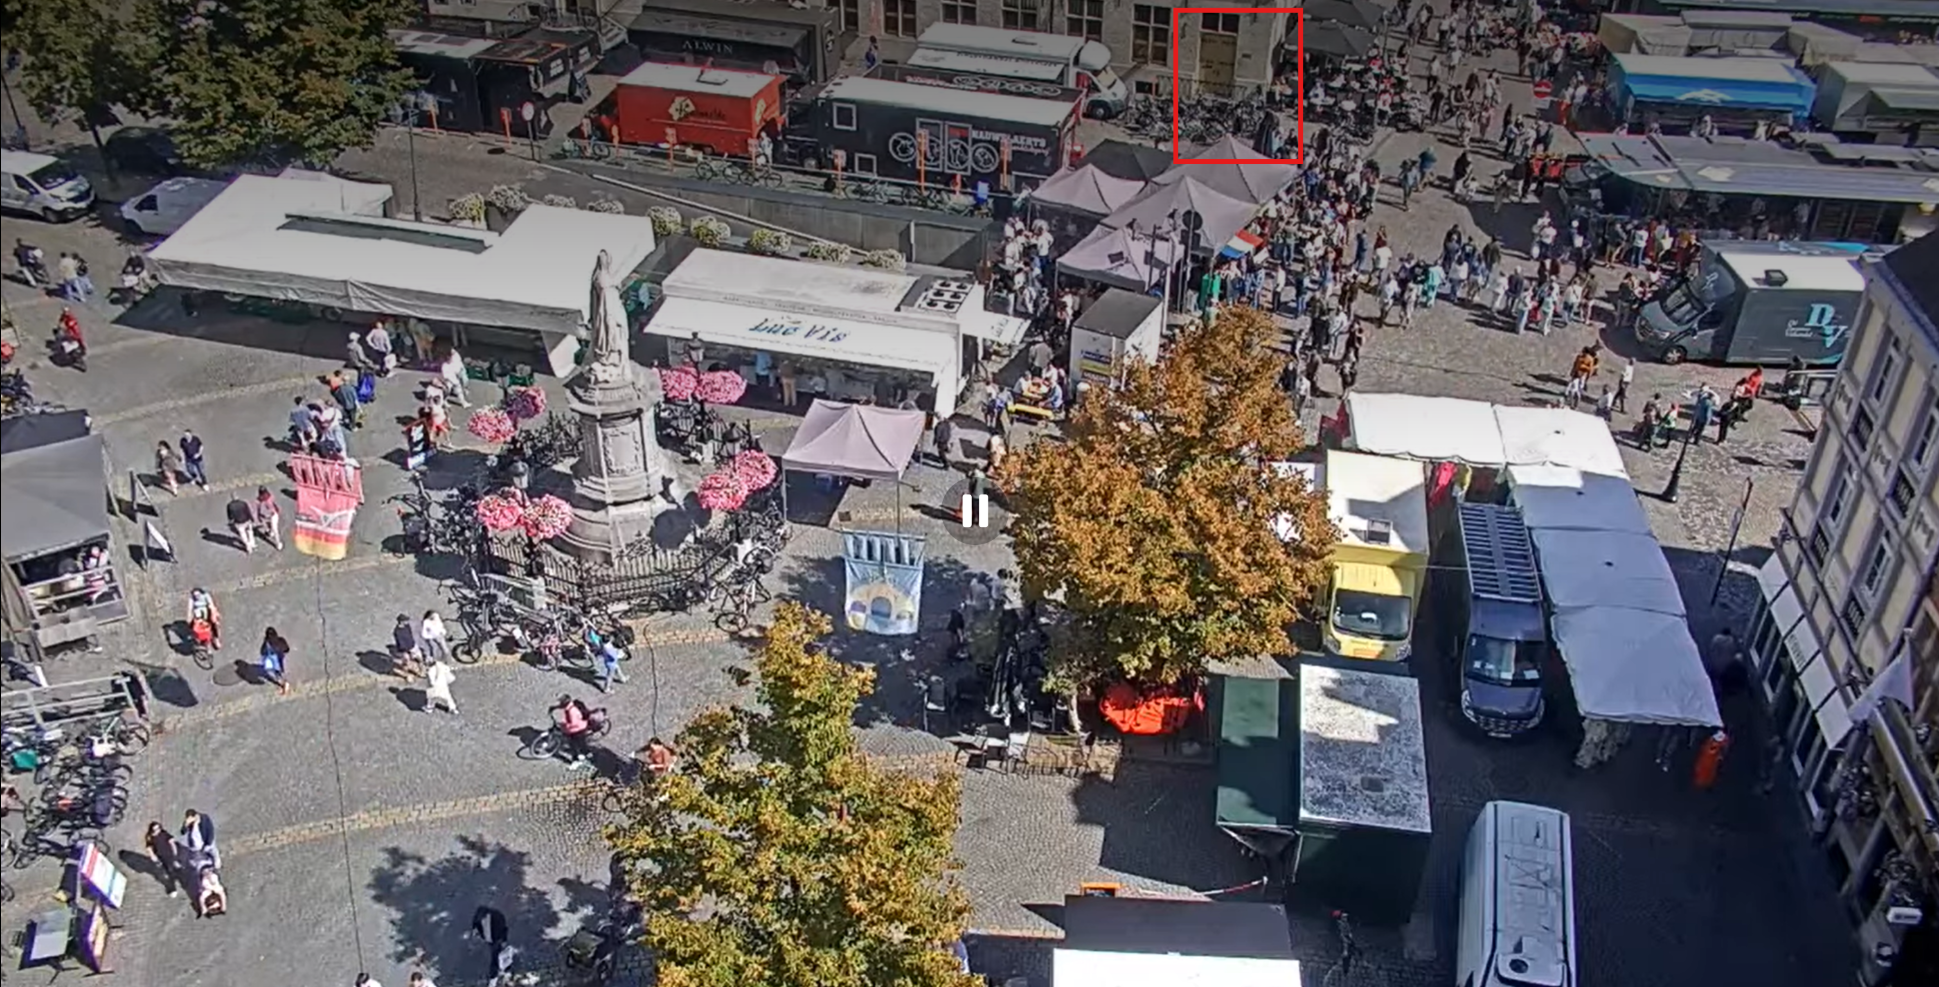
Challenge: You are an intelligence operative working with an underground network of spies. One of your field agents has secretly shared a photograph with you. Your first objective is to determine the geographical coordinates of the location by carefully analyzing the image. Look for clues such as architecture, terrain, vegetation, roads, landmarks, and other regional characteristics.
Flag format: the required coordinate format is 1.234, 2.234; the final flag should therefore be flag{1.234_2.234}
Walkthrough: Reverse image searching the provided photograph leads to the Schoenmarkt square in Mechelen, Belgium, with the original image available on Wikimedia Commons. Pivoting to OpenStreetMap/Street View and matching the buildings and surrounding landmarks corresponding to the red box in the challenge image pinpoints the camera location, giving coordinates rounded to three decimal places: 51.028, 4.479.
Flag: flag{51.028_4.479}
Name: The Missing Timestamp - 2 | Category: Chronolocation | 200 pts
Challenge: Intelligence indicates that the target entered the marked building shortly after this photograph was captured. Unfortunately, the CCTV system does not record timestamps. Your second objective is therefore to determine the approximate time at which the photograph was taken. The photograph was captured sometime between 20 August and 22 August.
Flag format: if the answer is around 8:00 AM to 9:00 AM, the flag would be flag{8:00_9:00}
Walkthrough: With the location already known and the capture window narrowed to 20–22 August, use the Sun's position and the visible tree/shadow geometry to estimate the capture time. Opening SunCalc at the identified coordinates and testing the possible dates in the given window allows the Sun's azimuth, altitude, and shadow length to be examined at different times. Comparing this to the shadow/tree geometry visible in the photograph, the image is consistent with a capture time of approximately 11:00 AM–12:00 PM.
Flag: flag{11:00_12:00}
Note: "Domain Owner Hunt" (historical WHOIS lookup) could be visualized using Maltego Graph connecting a domain node to its historical WHOIS registrant data. It's the same category as "The Counterfeit Web - 1" — ownership/attribution investigation (domain → WHOIS owner), using Maltego's Transforms for WHOIS history lookups.
Name: Domain Owner Hunt | Category: Threat Intelligence | 200 pts
Challenge: You work for a newly established OSINT services company that is looking to acquire osint.com as its primary domain name. During the initial investigation, your team encounters two obstacles: (1) the website is currently offline, and (2) the domain's WHOIS registration details have been redacted. Your task is to conduct an OSINT investigation to identify the domain owner and obtain a means of contact.
What is the email address associated with the domain owner of osint.com?
Answer format: flag{example@email.com}
Walkthrough: Searching the historical WHOIS records for osint.com using Whoxy reveals the associated person's name and email address.
Flag: flag{karthikmanimaran@gmail.com}
Name: Tracing the Family Connection | Category: Geolocation | 100 pts
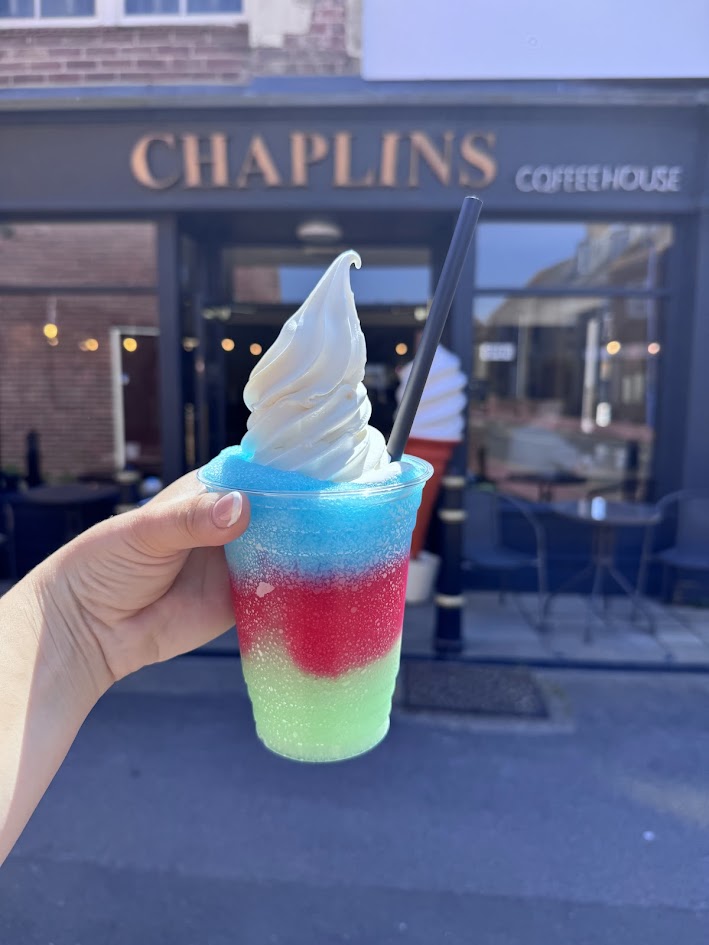
Challenge: During an investigation into the suspect's family and associates, investigators discovered that the suspect's sister had previously posted a photograph online. The image may contain visual and contextual clues that can help establish her whereabouts. Determining the city where the suspect's sister lives could provide investigators with a valuable lead for narrowing down the suspect's potential location.
In which city does the suspect's sister live?
Answer format: flag{city}
Walkthrough: A reverse image search, or simply reading the store name visible in the background, leads to identifying the coffee house as Chaplins Coffee House. Searching this name reveals multiple locations worldwide with Google Places listings; one of the top results reveals the same coffee house in Selsey, where a review containing the same image can be found.
Flag: flag{selsey}
Name: Tracking the Suspect's Vehicle | Category: Geolocation | 100 pts
Challenge: A further investigation into the suspect's movements led analysts to a Facebook Marketplace listing for a vehicle believed to be associated with the suspect.
Link: https://www.facebook.com/marketplace/np/item/2162197564627914/?location_id=108276092536515
What was the name and number of the street where the suspect's car was parked?
Answer format: flag{streetname_housenumber}
Walkthrough: Opening the provided link displays a car with a Dutch license plate and reveals that the listing location is Ede, Netherlands. Examining the uploaded photos shows the car was located at a car wash displaying the name KwikFit, a vehicle servicing and repair company. Searching "KwikFit Ede" on Google Maps reveals a location matching the same visual features shown in the Facebook car listing.
Flag: flag{Klaphekweg_18}
Name: Deleted Account Trail | Category: Social Media | 100 pts
Challenge: During an OSINT investigation into the suspect's online network, you discovered evidence of an interaction with a now-deleted Twitter/X account using the username "johnanitta." Although the account is no longer accessible, you believe that historical records and publicly available digital traces may reveal information that was previously associated with the account.
Identify the email address associated with the deleted Twitter/X account "johnanitta."
Flag format: flag{email@example.com}
Walkthrough: Searching for the X (Twitter) username "johnanitta" in a Twitter data leak, either locally or through a free online service such as Breach.vip, reveals the associated email address.
Flag: flag{john_venchalil@yahoo.co.in}
Name: Tracing the Artist | Category: Social Media | 100 pts
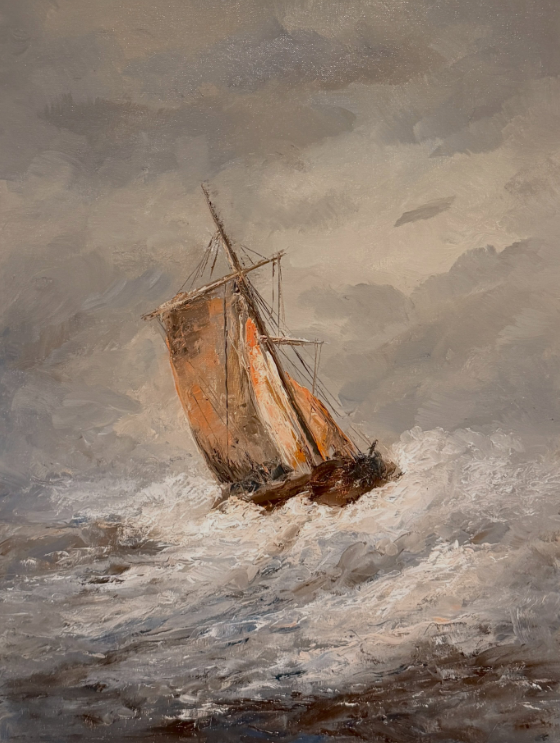
Challenge: During an OSINT investigation, analysts discovered an image of a distinctive piece of artwork believed to have been shared on Instagram. The original post may provide an important connection to the investigation, but the account behind it is unknown.
What is the Instagram ID of the account that originally posted this artwork?
Answer format: flag{12346579}
Walkthrough: A reverse image search leads to multiple paintings using the same image. Examining the search results reveals an Instagram account with the username "harutsarts" among the top results. Inspecting the page source code, or using an Instagram ID finder service such as CommentPicker, retrieves the account ID.
Flag: flag{53710212290}
Name: Who Took the Shot? | Category: Geolocation | 200 pts
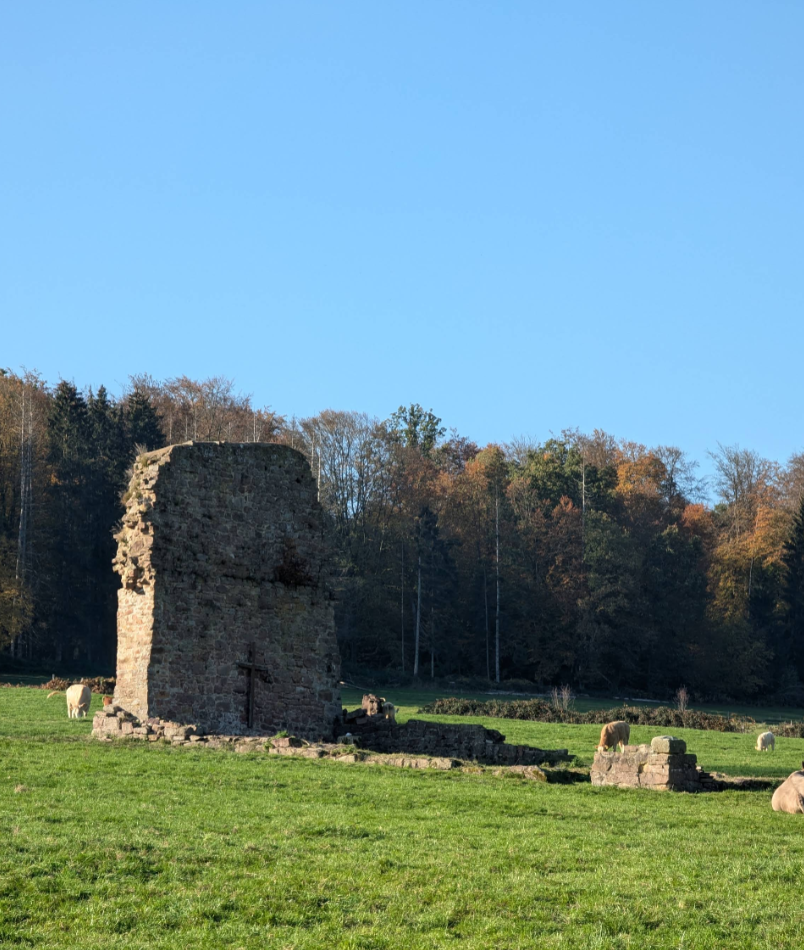
Challenge: During an OSINT investigation, analysts discovered a photograph believed to be connected to the suspect's movements. The same image may have been publicly uploaded to Google Maps, and identifying its contributor could reveal an important lead.
What is the name of the user who uploaded this picture to Google Maps?
Answer format: flag{first_last}
Walkthrough: A reverse image search reveals the location as "Kirchenruine Malliehagen." Searching this name leads to a Google listing with approximately 12 reviews; examining the reviews reveals the same image attached to the challenge, uploaded by Martina Simon.
Flag: flag{Martina_Simon}
Name: The Anonymous Tip | Category: Geolocation | 200 pts
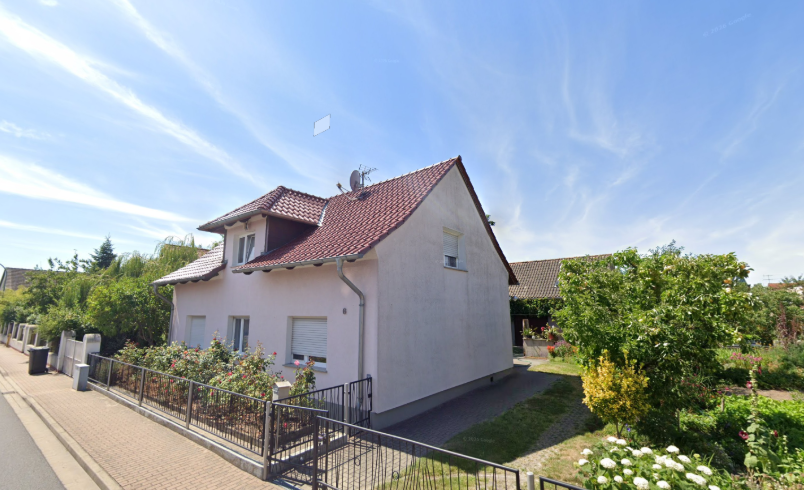
Challenge: During the investigation, police received an anonymous tip claiming that the suspect was living somewhere in Elster (Elbe). The source did not provide an exact address, leaving investigators to verify the information using publicly available clues and geolocation techniques.
What is the name of the street in Elster (Elbe) where the suspect lives?
Answer format: flag{streetname_housenumber}
Walkthrough: Examining the provided image reveals that the house number is 6. Since the location Elster (Elbe) is already known, use OpenStreetMap or the Bellingcat OpenStreetMap search tool to find all buildings with the number 6 in the area, then check each location using street view to identify the correct building.
Accepted flags:
flag{Gielsdorfer_6}flag{Gielsdorferst._6}flag{Gielsdorferst_6}flag{GielsdorferStraße_6}flag{GielsdorferStreet_6}
Name: The Stolen Mask | Category: Geolocation | 300 pts
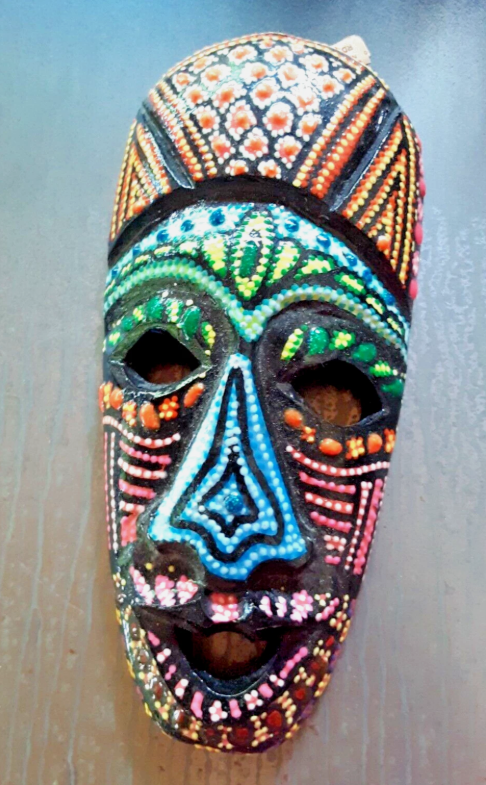
Challenge: A valuable wooden mask has been stolen from a museum, and police have launched an investigation to recover the artifact and identify those involved. Investigators received intelligence suggesting that the stolen mask was later offered for sale somewhere on the internet.
What is the username of the seller who listed the stolen wooden mask for sale online?
Answer format: flag{username}
Walkthrough: Searching for "wooden mask" on eBay and applying the Sold Items filter displays previously sold wooden masks. Looking back to 16 August 2026 reveals the same wooden mask listing, titled "Hand Painted Colorful Wooden Mask 7" Wall Mounted," along with the seller's username, "gaylen64."
Link: https://www.ebay.com/itm/196856418032
Flag: flag{GAYLEN64}
Name: Behind the Infrastructure | Category: Due Diligence | 100 pts
Challenge: As part of a corporate intelligence assessment of GFS Car Parts, your team is mapping key employees and their publicly available professional contact information. One person of interest is responsible for managing the company's IT infrastructure, but their business contact details are not immediately visible.
What is the business email address of the IT Infrastructure Manager at GFS Car Parts?
Answer format: flag{email@example.com}
Walkthrough: Searching for GFS Car Parts leads to its official website. Navigating the website reveals a "Corporate Information" page at the bottom, showing that the company belongs to the GFS Group. Searching for GFS Group leads to the group's official website, gfsgroup.com. Using Hunter.io identifies the company's corporate email addresses along with the corresponding roles associated with each address.
Flag: flag{mark.clements@gsfgroup.com}
Note: "Behind the Infrastructure" (finding a company's corporate email pattern via Hunter.io) could be visualized using Maltego Graph connecting a domain to discovered email addresses and their naming pattern. It's a standard email-discovery pivot (domain → email pattern), using Maltego's Hunter.io-style data partner Transforms.
Name: Before the Registration - 1 | Category: Due Diligence | 100 pts
Challenge: While researching the early history of Daniel Wellington, analysts discovered that the company's website has changed significantly since the brand first began selling watches. Information about its earliest products is no longer readily visible on the current website.
What was the price in USD listed on the website for the first Daniel Wellington watches?
Answer format: flag{550}
Walkthrough: Use the Wayback Machine to navigate to the first snapshot of the website, then click "Collection," which displays four watches, each priced at $145.
Link: https://web.archive.org/web/20111016174959/http:/www.danielwellington.com/collection/
Flag: flag{145}
Name: Before the Registration - 2 | Category: Due Diligence | 200 pts
Challenge: A due-diligence review of the previously mentioned company (Daniel Wellington) has uncovered an unusual discrepancy. Investigators discovered evidence suggesting that the company's online presence may have existed before the company was legally established. Determine the exact number of days between the creation of the company's website and its official registration date.
Notes: (1) The date format on the Swedish companies registration office is YYYY-MM-DD. (2) The calculation should exclude the end date.
Answer format: flag{123}
Walkthrough: First, identify the company's country of origin (Sweden) and search the Swedish company registry (https://foretagsinfo.bolagsverket.se/sok-foretagsinformation-web). Searching for the company name provides the Business ID 556875-5937 and registration date 2011-12-09. Next, use a WHOIS lookup service such as who.is to determine when the domain was registered: 16 February 2011. Using a Days Calculator (such as Time and Date's) to calculate the difference between 16 February 2011 and 9 December 2011 gives the required number of days.
Flag: flag{296}
Name: Following the Funding Trail | Category: Due Diligence | 200 pts
Challenge: Financial records can reveal important details about an organization's history that may not appear on its official website. Your task is to investigate publicly available records related to the nonprofit organization United Protestant Church Inc. and trace information about a government loan it received.
Determine the date on which United Protestant Church Inc.'s government loan was approved.
Answer format: flag{DD/MM/YYYY} — example: flag{15/06/2005}
Walkthrough: To find loans received by a company or organization, search government PPP (Paycheck Protection Program) loan records. A Google search for "PPP loan lookup" returns several websites offering access to these records; one useful resource is ProPublica, where searching for the organization United Protestant Church provides details such as the loan amount, approval date, and lender.
Flag: flag{28/04/2020}
Name: A Previous Employee | Category: Due Diligence | 200 pts
Challenge: Investigators mapping the target's network identified a possible connection to a bar staff member who worked at the MFC Foundation. Little is known about this individual, except for one key detail: they worked at the bar for approximately one and a half years.
What is the full name of the person who previously worked at the MFC Foundation for approximately one and a half years?
Answer format: flag{first_last}
Walkthrough: A Google search using the operators site:linkedin.com "MFC Foundation" "bar staff" or site:linkedin.com "MFC Foundation" "bar" returns relevant LinkedIn results, including an account belonging to Aimee Norster.
Link: https://www.linkedin.com/in/aimee-norster/
Flag: flag{AIMEE_NORSTER}
Name: Behind Cloudflare - 1 | Category: Threat Intelligence | 200 pts
Challenge: While investigating coinbase.com's historical infrastructure, investigators found that it is now protected by Cloudflare, obscuring its origin infrastructure. Historical DNS data may reveal what services the domain relied on in the past and how its infrastructure looked before those changes were introduced.
Can you name either one of the two MX records associated with the Coinbase domain in 2016?
Answer format: flag{ams.inline.email.example.fictional}
Walkthrough: Find a service that provides historical DNS records, including records from 2016 — a free service such as DNSHistory.org can be used to view the website's historical DNS information and identify the MX records associated with the domain at that time.
Accepted flags:
flag{smf.inline.email.fireeyecloud.com}flag{iad.inline.email.fireeyecloud.com}
Name: Behind Cloudflare - 2 | Category: Threat Intelligence | 300 pts
Challenge: What was the first publicly recorded IP address associated with coinbase.com after the website launched and before it began using Cloudflare?
Note: Use the earliest public IP recorded after Coinbase's website became publicly available.
Answer format: flag{10.6.59.12}
Walkthrough: First, determine when Coinbase.com became publicly available, using the Wayback Machine to examine the earliest snapshots and identify when a publicly accessible front-end page first appeared. Snapshots from 8 February 2011 and 17 May 2011 do not contain a publicly accessible front-end website, but the snapshot from 23 May 2012 does — making that the earliest snapshot showing a public-facing website. Next, identify the earliest IP address associated with the domain after that date using the IP History tool provided by ViewDNS.info (login required for full historical records). The results show 23.21.78.39 associated with the domain on 29 June 2012, the earliest identified after 23 May 2012.
Flag: flag{23.21.78.39}
Note: "Behind Cloudflare - 1 & 2" (uncovering the origin server hidden behind Cloudflare) could be visualized using Maltego Graph connecting a domain to its historical DNS/MX records and the historical IP address predating Cloudflare. It's a classic infrastructure investigation (domain → historical DNS/IP), using Maltego's Transforms for querying Domain/DNS history.
Name: Behind the University VPN | Category: Threat Intelligence | 300 pts
Challenge: You work as an OSINT Threat Intelligence Analyst for the University of London, where your team is assessing the institution's externally exposed infrastructure. As part of the assessment, you have been tasked with mapping the university's remote-access footprint and identifying infrastructure that could be discovered by external threat actors.
What is the Autonomous System Number (ASN) associated with the VPN infrastructure?
Answer format: flag{AS123}
Walkthrough: Searching for the University of London leads to its official website, london.ac.uk. Enumerating its subdomains using a subdomain discovery service such as Subdomain Finder (C99.nl) reveals multiple associated subdomains; searching for the keyword "VPN" identifies vpn.london.ac.uk, which resolves to IP address 128.86.200.179. Performing an ASN lookup on this IP using a service such as MXToolBox identifies the Autonomous System.
Links: https://subdomainfinder.c99.nl/scans/2026-09-13/london.ac.uk | https://mxtoolbox.com/SuperTool.aspx?action=asn:128.86.200.179
Flag: flag{AS786}
Note: "Behind the University VPN" (subdomain enumeration → IP → ASN) could be visualized using Maltego Graph chaining subdomain discovery transforms into IP resolution and then ASN lookup. It's a classic infrastructure pivot (subdomain → IP → ASN), using Maltego's Transforms for DNS/Netblock/ASN resolution back to back.
Name: Before It Vanished | Category: Social Media | 100 pts
Challenge: During an OSINT investigation, analysts came across references to the Instagram account "0.51__k," which has since been deleted. Investigators believe the profile's bio contained a reference to another account that could provide a valuable lead.
What username was mentioned in the bio of the deleted Instagram profile 0.51__k?
Answer format: flag{@username}
Walkthrough: With the Instagram username @0.51_\\\\\_k, construct the corresponding profile URL (instagram.com/0.51\\\\\_\\\\\\_k) and search for it on Archive.today. An archived snapshot from 24.11.2025 reveals the username "ey.olly\\\\\\_" in the profile bio.
Link: https://archive.ph/AQ06m
Flag: flag{@EY.OLLY_}
Name: Crossing the Social Trail | Category: Social Media | 100 pts
Challenge: During an OSINT investigation, analysts identified an Instagram profile associated with a person of interest. Investigators believe the individual also maintains a presence on Facebook, and correlating the accounts could help map their broader social-media footprint.
Determine the Facebook User ID associated with the person behind the Instagram account @jeanpi_garcia.
Answer format: flag{1000000123123123}
Walkthrough: Searching by the Instagram display name "Jean Paul Garcia" on Facebook reveals a profile with the same profile picture as the Instagram account. The Facebook User ID can then be retrieved by examining the page's source code or using an online lookup service such as Comment Picker.
Flag: flag{100036981857087}
Name: Birthday Breadcrumbs | Category: Social Media | 300 pts
Challenge: During an OSINT investigation, analysts identified an Instagram account (ID: 45432636478) belonging to a person of interest. The profile does not directly reveal their date of birth.
Using OSINT, determine the account owner's full date of birth.
Format: DD/MM/YYYY | Answer format: flag{20/03/2001}
Walkthrough: A public ID lookup and Instagram metadata resolve the numeric ID 45432636478 to @sydney.prince21. Public sources, including the Davis & Elkins College women's basketball roster, link the account to Sydney Prince, a basketball player from Sunderland, Maryland. A team birthday post states "Happy Birthday Sydney!" associated with 14 December 2025, establishing the day and month. Searching "Sydney Prince" "Davis & Elkins" leads to her profile on the official Davis & Elkins College website, listing her hometown as Sunderland, Maryland. Searching "Sydney Prince" in Sunderland, Maryland using TruePeopleSearch) returns one relevant record indicating a birth month of December and birth year of 2006. Cross-referencing both sources gives the full date of birth.
Flag: flag{14/12/2006}
Name: Competitive Intelligence | Category: Infrastructure Intelligence | 200 pts
Challenge: As a threat intelligence analyst assessing the external digital footprint of the defense contractor "Integration Services Incorporated," your team is building a technology profile of the organization.
Determine which network switch and its vendor are used by the company.
Answer format: flag{vendor_switch} — example: flag{Dell_PowerSwitch}
Walkthrough: Searching for the company name along with keywords such as "career" or "jobs" leads to the job listings page on the company's official website. Opening the System Administrator job listing and reviewing the job requirements states that the applicant should be able to maintain computer lab infrastructure, including Cisco Catalyst equipment.
Flag: flag{CISCO_CATALYST}
Keep Learning, Keep Investigating! 🔗︎
That wraps up our Qualifier A walkthrough! We hope it helped you understand the reasoning behind the solutions and discover techniques you can apply in your next investigation.
Did you take a different route to a flag or find a useful source we haven’t covered? Share your approach in our Discord community or email us at community@maltego.com. Comparing methods and discussing dead ends helps everyone learn.
Ready for Qualifier B in November? Stay tuned for announcements on **Discord **and our CTF page. In the meantime, use these walkthroughs to practice your methods, sharpen your verification skills, and prepare for a fresh set of clues.
Keep practicing, share what you learn, and we’ll see you in the next round!